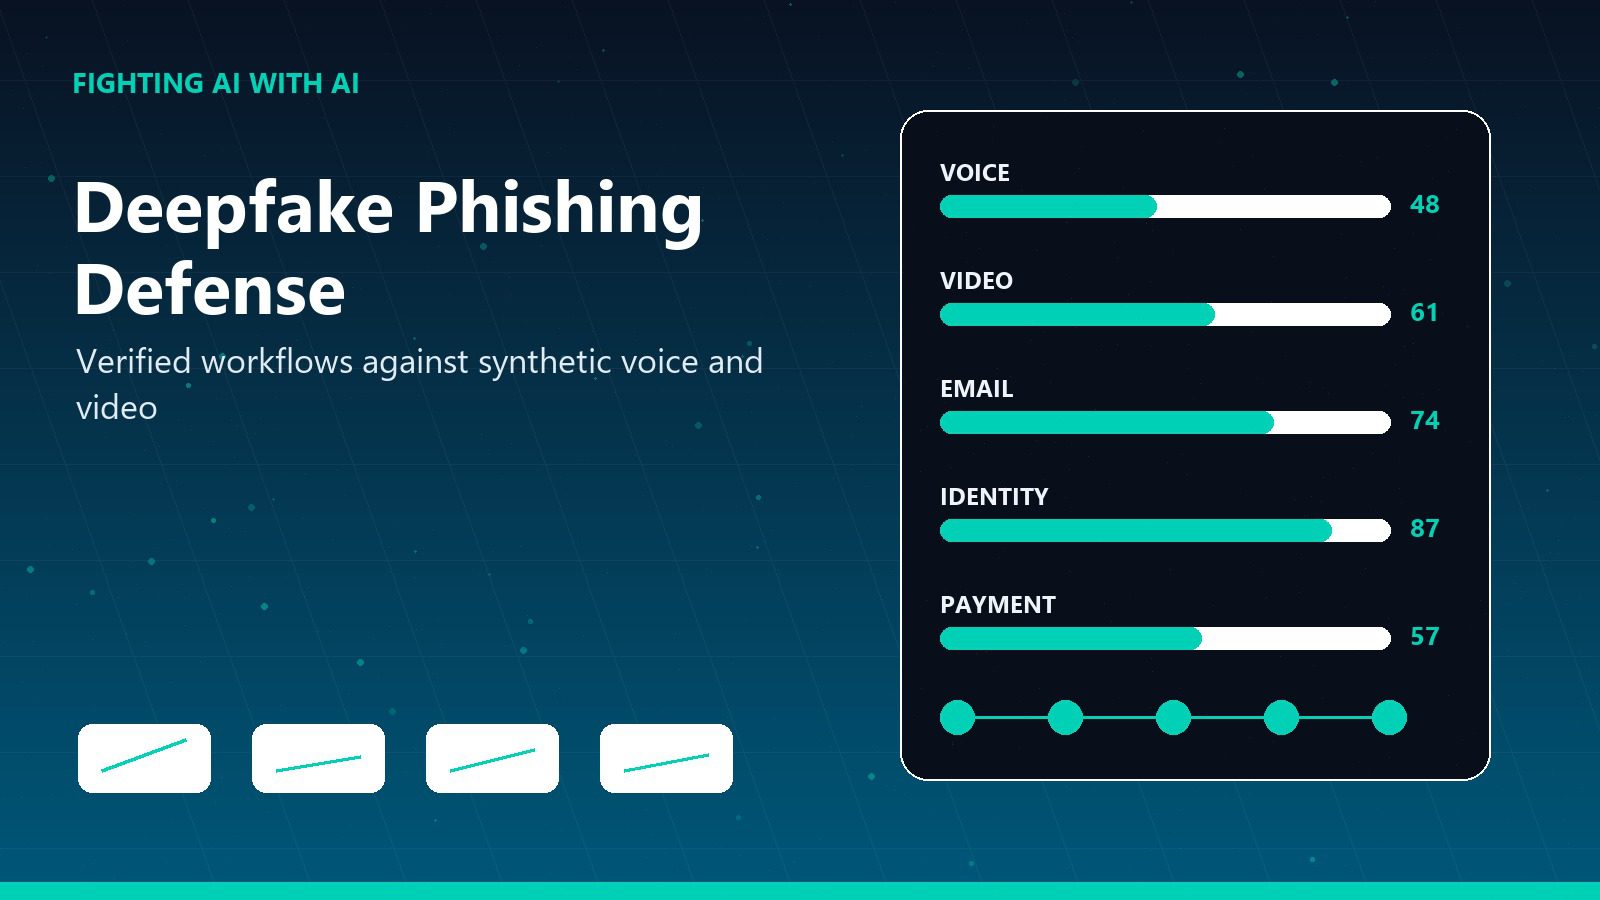
Fighting AI with AI: 7 Powerful Deepfake Defenses
Fighting AI with AI guide for defending against deepfake phishing and cloned-voice social engineering with verification workflows, AI detection, training, and governance.

Fighting AI with AI guide for defending against deepfake phishing and cloned-voice social engineering with verification workflows, AI detection, training, and governance.
Small law firms handle confidential client files, payment records, litigation material, discovery data, tax information, contracts, and sensitive communications. These seven IT security compliance frameworks help firms build a practical security roadmap without copying an enterprise program that is too heavy to maintain.
A localized ransomware attack does not always mean every file is gone. The safest recovery path is to isolate affected systems, preserve evidence, confirm clean recovery sources, restore carefully, and close the entry point before reconnecting.
International data privacy compliance is difficult because laws, transfers, vendors, consent rules, AI systems, and breach duties overlap. Use these seven moves to turn legal complexity into operating discipline.
Enterprise ransomware attacks do not happen only because leaders are careless. They happen when complex systems, incentives, identity gaps, vendor exposure, and untested recovery plans give criminals leverage.
Incident response plan testing gives security, IT, legal, communications, and business teams a safe way to rehearse cyber disruption before real pressure arrives.
A practical guide to connected facility risk, smart building devices, access control, cameras, lighting systems, network segmentation, and converged security governance.
A practical guide to deploying eBPF security observability across Kubernetes clusters for syscall tracing, runtime threat detection, policy tuning, and incident response.
A practical implementation guide for confidential computing platforms, secure hardware enclaves, attestation, key release, tenant isolation, and cloud governance.
A practical guide to moving beyond threat blocking and building operational continuity, breach readiness, and recovery capability across critical services.










