How to Set Up AnythingLLM: A Beginner-Friendly Setup Guide
A beginner-friendly guide to setting up AnythingLLM for document search, chat, and private AI workflows using desktop or Docker.

A beginner-friendly guide to setting up AnythingLLM for document search, chat, and private AI workflows using desktop or Docker.

🟠 High ⏱ 15–60 min Last verified: 9 April 2026 Affected versions: Oracle Linux 10 📖 ~4 min read • Source: ELSA advisory ELSA-2026-50254 Related CVEs: CVE-2026-31431 Table of contents Symptom & Impact Environment & Reproduction Root Cause Analysis Quick Triage Step-by-Step Diagnosis Solution – Primary Fix Solution – Alternative Approaches Verification & Acceptance […]
A practical guide to setting up Agent S3 through Agent-S, including OCR, model access, grounding setup, and first computer-use tests.
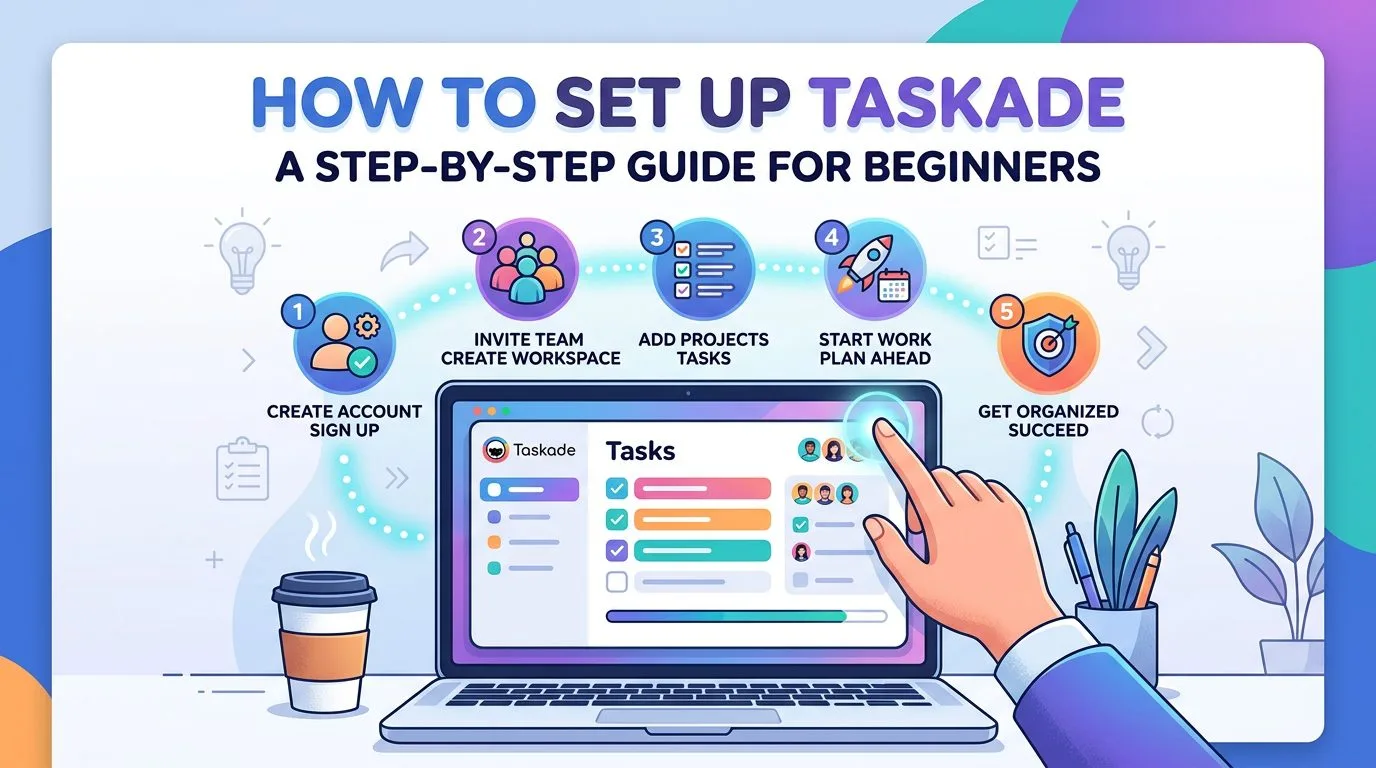
Learn how to set up Taskade step by step. Create your workspace, projects, views, templates, and automations so you can organize personal or team work faster.

🟢 Low ⏱ 5–15 min Last verified: 8 April 2026 Affected versions: FreeBSD 15 📖 ~4 min read • Source: FreeBSD VuXML VuXML topic: vim — Vim Shell Command Injection Vulnerabilities Related CVEs: CVE-2007-2953 CVE-2008-2712 Upstream summary: Rdancer.org reports: Improper quoting in some parts of Vim written in the Vim Script can lead to […]

🟢 Low ⏱ 5–15 min Last verified: 8 April 2026 Affected versions: FreeBSD 15 📖 ~4 min read • Source: FreeBSD VuXML VuXML topic: wu-ftpd — remote globbing DoS vulnerability Related CVEs: CVE-2004-0148 CVE-2005-0256 Upstream summary: An iDEFENSE Security Advisory reports: Remote exploitation of an input validation vulnerability in version 2.6.2 of WU-FPTD could […]

🟡 Medium ⏱ 10–30 min Last verified: 25 May 2026 Affected versions: NetBSD 10.0 📖 ~4 min read • Source: pkgsrc audit-packages entry Related CVEs: CVE-2025-31500 CVE-2025-31501 CVE-2025-30087 CVE-2025-9158 CVE-2025-61873 Upstream summary: pkgsrc audit-packages flagged rt5<5.0.8 for vulnerability class 'cross-site-scripting'. Reference: https://nvd.nist.gov/vuln/detail/CVE-2025-31500 Table of contents Symptom & Impact Environment & Reproduction Root Cause Analysis […]

🟢 Low ⏱ 5–15 min Last verified: 8 April 2026 Affected versions: FreeBSD 12 📖 ~4 min read • Source: FreeBSD VuXML VuXML topic: py-social-auth-app-django — Unsafe account association Related CVEs: CVE-2024-32879 CVE-2025-61783 Upstream summary: Michal Čihař reports: Upon authentication, the user could be associated by e-mail even if the associate_by_email pipeline was not […]

🟢 Low ⏱ 5–15 min Last verified: 8 April 2026 Affected versions: FreeBSD 15 📖 ~4 min read • Source: FreeBSD VuXML VuXML topic: p5-Dancer — possible to abuse session cookie values Upstream summary: Russell Jenkins reports: It was possible to abuse session cookie values so that file-based session stores such as Dancer::Session::YAML or […]

🟡 Medium ⏱ 10–30 min Last verified: 25 May 2026 Affected versions: NetBSD 10.0 📖 ~4 min read • Source: pkgsrc audit-packages entry Related CVEs: CVE-2025-1735 Upstream summary: pkgsrc audit-packages flagged php82-pgsql<8.2.29 for vulnerability class 'sql-injection'. Reference: https://nvd.nist.gov/vuln/detail/CVE-2025-1735 Table of contents Symptom & Impact Environment & Reproduction Root Cause Analysis Quick Triage Step-by-Step Diagnosis […]










