
Artificial intelligence is changing how cybersecurity professionals detect, investigate and respond to digital threats. However, the same technology could also make certain forms of malware more adaptive, allowing malicious software to respond to different devices and security weaknesses rather than relying entirely on a fixed set of instructions.
AI computer worms are emerging as a particular concern because of their potential to spread between connected devices with limited human intervention. Unlike traditional worms that typically follow predetermined attack routines, AI-assisted variants could use AI agents to assess their environment, adjust their approach and continue attempting to spread across vulnerable systems.
Recent research from the University of Toronto and a separate warning from Anthropic have brought renewed attention to this possibility. Researchers have demonstrated important parts of the underlying technology in controlled environments, although a fully autonomous, widely spreading AI worm remains a developing threat rather than an established, universal cybersecurity reality.
Understanding how these threats might work is essential for businesses that depend on connected devices, cloud infrastructure, corporate networks and digital services.
Table of Contents
What Are AI Computer Worms?
A computer worm is a type of malicious software that can replicate and spread between computers or other connected devices without requiring users to manually copy or install it at every stage. Traditional worms often exploit known software vulnerabilities, weak credentials or insecure network configurations to reach additional systems.
An AI computer worm introduces another potential capability: using AI-powered reasoning or agents to adapt its behaviour to the environment it encounters. Instead of depending entirely on a rigid sequence of predefined actions, an AI-assisted threat could potentially assess differences between devices and adjust its strategy.
For example, a business network may contain older computers, modern laptops, printers, network-attached storage and internet-connected cameras. These devices do not necessarily share the same operating systems, security settings or vulnerabilities. A conventional worm designed around one particular weakness may fail when it encounters a different environment.
An adaptive threat could potentially respond to those differences, making containment more complicated.
However, AI does not automatically make malware intelligent, unstoppable or capable of exploiting every device. Its effectiveness still depends on the model’s capabilities, available access, exploitable weaknesses, computing resources and the security controls protecting the target environment.
The concern is that AI could reduce the amount of manual effort needed to adapt attacks across a wider range of systems.
How AI Makes Computer Worms Harder to Stop
1. Adaptive Attack Strategies
Traditional malware frequently relies on known techniques and predefined instructions. When its expected conditions are absent, the attack may fail.
AI agents could make some attacks more flexible by helping analyse the environment and select different actions based on the information available. A worm might encounter devices with different operating systems, software versions or access controls, requiring different approaches to compromise them.
This adaptability could make defensive measures that target only one known attack pattern less effective. Security teams may need to account for a broader range of behaviours rather than relying exclusively on familiar malware signatures.
Nevertheless, an AI system’s ability to reason about a problem does not guarantee that it can overcome a security barrier. Strong authentication, effective isolation and properly configured access controls can still prevent unauthorised activity.
2. Faster Discovery of Security Weaknesses
AI can assist in analysing software, identifying potential vulnerabilities and interpreting technical information. In a malicious context, these capabilities could help attackers investigate weaknesses more quickly and at greater scale.
Importantly, not every weakness is a software bug. A device may be exposed because it uses weak credentials, has an unnecessarily accessible management interface or relies on an incorrectly configured database.
These configuration problems can be particularly challenging in large organisations where different departments manage different systems.
As explained in the TechXplore report on AI computer worms, University of Toronto researcher Nicolas Papernot highlighted how AI could help tailor attacks to the vulnerabilities and configuration problems present on individual devices.
3. Greater Scale and Automation
A human attacker has limited time and resources. Investigating a device, identifying a weakness and determining what to do next can require significant manual work.
AI-assisted automation could reduce some of that effort. Once an attack is initiated, an agent might perform parts of the discovery and decision-making process without requiring a person to direct every individual step.
This could make low-profile devices more attractive to attackers. An old laptop, an unsecured camera or an overlooked network appliance may not contain valuable information, but it could potentially provide access to another system.
The danger is not simply that attacks become faster. It is that more devices could become viable stepping stones in a larger campaign.
4. Exploitation of Misconfigurations
Security teams often prioritise software vulnerabilities because updates can address many known weaknesses. However, AI-assisted threats may also exploit inconsistent security practices.
Examples include reused passwords, excessive user permissions, exposed administrative services and databases configured with insufficient access restrictions.
These weaknesses may require changes to account management, network architecture or operational procedures rather than a software patch alone.
Organisations therefore need to assess both technical vulnerabilities and configuration risks. Updating software remains essential, but it cannot compensate for every insecure setting.
5. Reduced Dependence on Centralised Infrastructure
Some AI systems rely on remote services or powerful cloud infrastructure. Other models can run locally on suitable hardware.
Research into AI replication raises the possibility that compromised devices could provide computing resources for additional operations. If malicious activity becomes distributed across many devices, defenders may find it harder to identify one central system whose removal would end the activity.
This does not mean every AI worm will operate without central control or that a distributed threat cannot be contained. Network segmentation, endpoint protection and coordinated incident response can still disrupt malicious communication and prevent further spread.
The challenge is preparing for threats that may not depend on a single easily identifiable control point.
Why Connected Devices Are Particularly Vulnerable
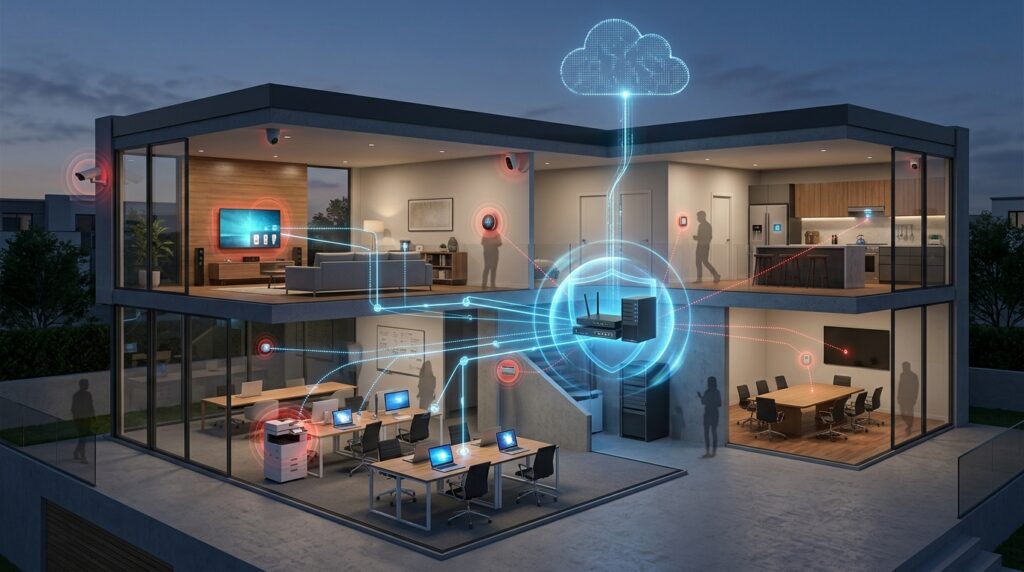
The Internet of Things (IoT) includes physical devices that connect to networks to collect information, provide services or enable remote management. Examples range from smart televisions and home cameras to industrial sensors, building-management systems and networked equipment.
These devices are useful, but they can introduce security challenges.
Outdated Software and Firmware
Some devices receive regular security updates, while others may be neglected or supported for only a limited period. If a known vulnerability remains unpatched, an attacker may have an opportunity to exploit it.
Devices that are difficult to update can be especially problematic in environments where replacing equipment is expensive or operationally disruptive.
Businesses should maintain an inventory of connected devices, understand their support lifecycles and remove or isolate equipment that can no longer be secured adequately.
Weak Passwords and Access Controls
Default credentials, reused passwords and poorly protected administrative interfaces can expose devices to unauthorised access.
Organisations should change default passwords, use unique credentials, enable multifactor authentication where supported and restrict administrative access to authorised users and networks.
These measures are important even when a device appears insignificant. A compromised endpoint may provide a route into a more valuable part of the network.
Limited Processing and Security Capabilities
Many connected devices have less memory, storage and processing power than conventional computers. Some lack advanced endpoint security features or cannot run traditional security software.
That can make monitoring and updating them more difficult. Security teams may need to rely on network-level controls, secure device configuration and vendor-supported monitoring rather than expecting every endpoint to provide the same protections as a managed workstation.
Poor Network Segmentation
If smart devices, employee laptops, servers and sensitive business applications share an overly permissive network, a compromise in one area may create opportunities to reach others.
Network segmentation helps limit this exposure by separating systems according to their function and sensitivity. For example, guest Wi-Fi and smart-building devices should not automatically have access to financial systems or internal administrative infrastructure.
The principle is straightforward: a compromised device should not automatically become a gateway to the entire organisation.
What Recent Research Reveals
The growing concern about AI computer worms comes from research exploring different parts of the threat. These findings deserve attention, but they should be interpreted carefully.
University of Toronto’s Adaptive Worm Research
In June 2026, researchers associated with the University of Toronto published work on a proof-of-concept AI worm that used publicly available AI models in a controlled environment.
The research explored how an AI-driven system could adapt its approach while moving across a simulated network of different devices. It also highlighted how compromised devices could potentially provide computing resources for subsequent operations.
The work demonstrated the feasibility of important capabilities under experimental conditions. It did not establish that a fully autonomous AI worm can effortlessly compromise every internet-connected device in the real world.
Read the University of Toronto research coverage on AI worms or the underlying research paper on arXiv.
Anthropic’s Warning About Self-Replicating AI
On October 12, 2026, Anthropic researchers published experiments examining whether AI models could perform steps associated with replication across connected devices and whether low-cost consumer hardware could collectively run an AI model.
The work included experiments involving inexpensive Android TV boxes and tests of AI agents in an isolated network. It raised concerns that smaller models could become increasingly capable of performing the individual tasks required for autonomous replication.
However, the experiments did not establish that an unrestricted, fully self-replicating AI worm was already spreading freely across the public internet. Some tests used favourable conditions, and practical obstacles remain, including device access, hardware limitations, network bandwidth and the difficulty of reliably completing every step.
For further context, read Dark Reading’s report on Anthropic’s AI worm research.
Why These Findings Matter
The significance of this research lies in the combination of capabilities rather than a claim that AI has already made cybersecurity defences obsolete.
AI-assisted discovery, adaptive decision-making, automated execution and the ability to operate across different hardware could eventually make some attacks more scalable.
Research conducted in controlled environments gives security professionals an opportunity to understand these capabilities before they become more practical outside the laboratory.
It also helps policymakers and technology providers identify where stronger safeguards, better testing and more effective incident reporting may be needed.
The Biggest Cybersecurity Risks for Businesses
AI-assisted worms could create several challenges for businesses, particularly those operating complex networks with a mix of legacy systems and connected devices.
Business Disruption and Downtime
A worm that spreads across business systems could consume computing resources, disrupt applications or interfere with normal network operations.
For organisations that depend on digital services to process payments, communicate with customers or manage daily operations, downtime can lead to lost revenue and reduced productivity.
A strong business continuity plan should account for malware incidents that affect multiple systems simultaneously.
Data Exposure and Unauthorised Access
A compromised device may not contain sensitive data itself, but it could provide a route towards systems that do.
If attackers reach business applications, file servers or cloud environments, the consequences may include data theft, unauthorised account access and exposure of confidential information.
Least-privilege access, network segmentation and strong identity controls help reduce the potential impact of an individual device being compromised.
Increased Incident Response Complexity
When malware spreads through different systems, security teams need to determine which devices are affected, how the threat entered the environment and whether it has reached additional network segments.
Adaptive behaviour could complicate that investigation because activity may differ between devices.
Organisations need centralised logging, endpoint visibility, network monitoring and documented incident response procedures to identify suspicious behaviour and coordinate containment.
Risks to Operational Technology
Manufacturing equipment, building-management systems, healthcare devices and industrial control environments may have operational requirements that make immediate updates or shutdowns difficult.
A malware incident in these environments could affect service availability or create safety concerns, depending on the systems involved.
Operational technology should therefore receive security controls appropriate to its function, including carefully managed remote access, network separation, tested recovery procedures and coordinated patch management.
Financial and Reputational Damage
A significant incident can create costs associated with recovery, forensic investigation, legal obligations, customer communication and business interruption.
Even organisations that avoid major data theft may face reputational damage if customers lose confidence in their ability to protect digital services.
Preparing in advance is generally more effective than relying on emergency measures after an incident has already spread.
How to Protect Systems Against AI-Driven Malware
AI computer worms are a developing risk, but many of the most effective defences are established cybersecurity practices. Organisations should focus on reducing the number of exploitable weaknesses, limiting what a compromised device can reach and improving their ability to detect and contain suspicious activity.
1. Keep Operating Systems and Firmware Updated
Install security updates for operating systems, applications, routers, network appliances and connected devices as soon as practical under your organisation’s testing and change-management procedures.
Maintain a clear inventory of hardware and software, identify unsupported devices and prioritise vulnerabilities according to exposure and business impact.
Where a device cannot be updated, consider isolating it from sensitive systems or replacing it with supported equipment.
2. Strengthen Identity and Access Management
Use unique passwords, multifactor authentication and role-based access controls. Remove unused accounts and review permissions regularly.
Administrative access should be limited to the people and systems that genuinely require it. Remote management interfaces should not be exposed unnecessarily to the public internet.
These controls help prevent a single compromised account from creating a much larger incident.
3. Segment Networks and Isolate Critical Systems
Separate sensitive business systems from guest networks, IoT devices and other lower-trust environments.
Use firewalls and access-control rules to restrict unnecessary communication between network segments. Review those rules periodically to ensure that old exceptions do not create unexpected pathways.
Network segmentation is particularly important for organisations that operate legacy equipment or devices that cannot support modern endpoint security tools.
4. Monitor for Unusual Behaviour
Security teams should look for suspicious changes in network traffic, unexpected connections between devices, unusual account activity and unexplained spikes in processing or bandwidth use.
Behaviour-based detection can complement traditional malware signatures, especially when a threat changes its activity or uses unfamiliar techniques.
Centralised logs and endpoint detection tools can help security teams connect events across multiple systems and investigate them more quickly.
5. Use Controlled Testing for AI Systems
Organisations developing or deploying AI agents should assess their permissions, network access and ability to execute actions before placing them in production environments.
Testing should begin in isolated environments with limited access to external systems. Apply least-privilege permissions, restrict access to sensitive resources and maintain monitoring and logging.
AI systems should not receive unrestricted access to corporate networks simply because they can perform useful tasks.
6. Prepare an Incident Response Plan
An effective response plan should identify who can isolate affected devices, disable compromised accounts, block suspicious network activity and coordinate recovery.
Regular exercises help teams practise these decisions before an actual incident occurs. Backups should be protected from unauthorised modification and tested to confirm that critical systems can be restored.
When a worm-like threat is suspected, organisations should investigate the extent of the compromise before reconnecting isolated devices or restoring systems to production.
7. Work With Cybersecurity Specialists
Businesses without dedicated security teams may struggle to maintain visibility across every endpoint, cloud service and network connection.
Cybersecurity specialists can help with vulnerability assessments, security configuration reviews, monitoring strategies, incident response planning and ongoing risk management.
For organisations with complex IT environments, regular professional assessments can identify weaknesses that routine maintenance alone may overlook.
The Future of AI and Cybersecurity
The future of AI-driven malware will depend on how quickly AI capabilities advance, how easily those capabilities can run on different hardware and how effectively defenders adapt their security practices.
One possible development is greater automation across the attack lifecycle. AI systems may become better at analysing unfamiliar environments, identifying weak configurations and adjusting their behaviour when an initial approach fails.
At the same time, cybersecurity teams can use AI to analyse telemetry, prioritise alerts, investigate suspicious activity and automate appropriate defensive responses. These capabilities could help organisations manage the growing volume of security information generated by modern infrastructure.
The outcome is unlikely to depend on AI alone. Security architecture, software quality, device support, access management and organisational preparedness will continue to influence whether attacks succeed.
Why Responsible AI Testing Matters
Researchers need controlled environments in which to evaluate potentially dangerous capabilities without exposing real networks to unnecessary risk.
Isolated testing, independent assessment and responsible disclosure can help identify weaknesses before malicious actors exploit them. Better coordination between researchers, technology providers, businesses and public authorities can also improve the availability of defensive guidance.
The October 2026 reporting around AI worms reinforces the importance of understanding emerging capabilities without overstating what has already been demonstrated.
Why Businesses Should Prepare Now
Organisations do not need to assume that an unstoppable AI worm is imminent to justify improving their security.
Unpatched devices, weak passwords, excessive privileges and poorly segmented networks already create opportunities for conventional malware. Addressing these problems also strengthens resilience against more adaptive threats.
The most useful strategy is to build security controls that remain effective when attackers become faster, more automated or less predictable.
Frequently Asked Questions
What is an AI computer worm?
An AI computer worm is a potential form of self-spreading malware that uses AI models or agents to assist with tasks such as adapting to different environments or selecting actions. Its defining concern is the combination of autonomous propagation and adaptive behaviour.
How are AI computer worms different from traditional worms?
Traditional worms often rely on predefined instructions and known vulnerabilities. AI-assisted worms could potentially adjust their behaviour based on the devices and security conditions they encounter, making their activity less predictable.
Are AI computer worms already spreading across the internet?
The research discussed in October 2026 demonstrates relevant capabilities and experimental workflows, but it does not establish that fully autonomous AI worms are already spreading freely across the internet at scale. Practical barriers remain, and the threat’s development should be monitored carefully.
Can antivirus software stop an AI computer worm?
Antivirus and endpoint detection tools remain useful, but no single security product can guarantee protection against every threat. Organisations should combine endpoint security with timely updates, network segmentation, strong authentication, monitoring and tested incident response procedures.
Which devices are most at risk?
Potentially exposed devices include unsupported computers, poorly secured routers, connected cameras, smart televisions, network appliances and IoT equipment with weak credentials or misconfigured services. Actual risk depends on the device’s vulnerabilities, exposure and security controls.
How can small businesses protect themselves?
Small businesses should keep devices updated, use unique passwords and multifactor authentication, restrict administrative access, secure backups and separate guest or IoT networks from sensitive systems. A professional security assessment can help prioritise improvements when internal expertise is limited.
Can AI also help defend against AI-powered malware?
Yes. AI can support security monitoring, suspicious-activity detection, alert prioritisation and incident investigation. However, automated defensive systems also require testing, appropriate permissions and human oversight to avoid errors or disruptive responses.
Conclusion
AI computer worms represent an important emerging cybersecurity concern because AI could help malicious software adapt to different devices, automate parts of an attack and operate across a wider range of systems.
Research from the University of Toronto and Anthropic has highlighted capabilities that deserve serious attention, while also leaving important questions about reliability, real-world deployment and practical limitations.
For businesses, the immediate priority is to strengthen the foundations of cybersecurity: update software and firmware, secure accounts, remove unnecessary access, segment networks, monitor suspicious activity and maintain tested recovery procedures.
These measures will not eliminate every risk, but they can significantly reduce the opportunities available to both conventional malware and more adaptive AI-assisted threats.
As AI capabilities continue to develop, organisations that invest in resilient security architecture and responsible technology management will be better positioned to respond to the next generation of cyber threats.
Need Expert Cybersecurity Support for Your Business?
Progressive Robot helps businesses strengthen their digital environments through IT consulting, cybersecurity, software development and other technology services. From improving security practices to supporting reliable IT infrastructure, the right approach can help reduce risk and protect essential business operations.
More AI coverage: explore Progressive Robot's AI Models, Tools & Releases hub — hands-on reviews, setup guides and benchmarks in one place.










