January 2026 - Page 23 of 150

NetBSD 9.4 — openbabel — multiple vulnerabilities (10 CVEs) — patch and remediation guide — diagnosis and fix on NetBSD 9.4

NetBSD 9.4 — openbabel — multiple vulnerabilities (10 CVEs) — patch and remediation guide

🟠 High   ⏱ 15–60 min  Last verified: 25 May 2026 Affected versions: NetBSD 9.4 📖 ~4 min read  •  Source: pkgsrc audit-packages entry Related CVEs: CVE-2025-10994 CVE-2025-10995 CVE-2025-10996 CVE-2025-10997 CVE-2025-10998 CVE-2025-10999 CVE-2025-11000 CVE-2026-2704  +2 more Upstream summary: pkgsrc audit-packages flagged openbabel-[0-9]* for vulnerability class 'use-after-free'. Reference: https://nvd.nist.gov/vuln/detail/CVE-2025-10994 Table of contents Symptom & Impact Environment […]

Read more
SLES 15 — glibc-livepatches — vulnerability — patch and remediation guide — diagnosis and fix on SLES 15

SLES 15 — glibc-livepatches — vulnerability — patch and remediation guide

🟠 High   ⏱ 15–60 min  Last verified: 28 January 2026 Affected versions: SLES 15 📖 ~4 min read  •  Source: SUSE advisory SUSE-SU-2026:1498-1 (see also SUSE bugzilla) Related CVEs: CVE-2026-4046 Upstream summary: The iconv() function in the GNU C Library versions 2.43 and earlier may crash due to an assertion failure when converting inputs […]

Read more
AlmaLinux 8 — dotnet8.0 — multiple vulnerabilities (20 CVEs) — patch and remediation guide — diagnosis and fix on AlmaLinux 8

AlmaLinux 8 — dotnet8.0 — multiple vulnerabilities (20 CVEs) — patch and remediation guide

🟠 High   ⏱ 15–60 min  Last verified: 25 May 2026 Affected versions: AlmaLinux 8 📖 ~4 min read  •  Source: AlmaLinux ALSA ALSA-2026:8468 Related CVEs: CVE-2026-26171 CVE-2026-32178 CVE-2026-32203 CVE-2026-33116 CVE-2026-26130 CVE-2025-55247 CVE-2025-55248 CVE-2025-55315  +12 more Upstream summary: .NET is a managed-software framework. It implements a subset of the .NET framework APIs and several new […]

Read more
Debian 13 — cacti — multiple vulnerabilities (20 CVEs) — patch and remediation guide — diagnosis and fix on Debian 13

Debian 13 — cacti — multiple vulnerabilities (20 CVEs) — patch and remediation guide

🟠 High   ⏱ 15–60 min  Last verified: 28 January 2026 Affected versions: Debian 13 (trixie) 📖 ~4 min read  •  Source: Debian Security Tracker Related CVEs: CVE-2002-1477 CVE-2002-1478 CVE-2002-1479 CVE-2004-1736 CVE-2004-1737 CVE-2005-10004 CVE-2005-1524 CVE-2005-1525  +12 more Upstream summary: graphs.php in Cacti before 0.6.8 allows remote authenticated Cacti administrators to execute arbitrary commands via shell […]

Read more
Amazon Linux 2 — cups — multiple vulnerabilities (15 CVEs) — patch and remediation guide — diagnosis and fix on Amazon Linux 2

Amazon Linux 2 — cups — multiple vulnerabilities (15 CVEs) — patch and remediation guide

🟠 High   ⏱ 15–60 min  Last verified: 25 May 2026 Affected versions: Amazon Linux 2 📖 ~4 min read  •  Source: Amazon Linux advisory ALAS2-2026-3279 Related CVEs: CVE-2026-34978 CVE-2026-34979 CVE-2026-34980 CVE-2026-34990 CVE-2025-58060 CVE-2024-47176 CVE-2025-58364 CVE-2023-4504  +7 more Upstream summary: OpenPrinting CUPS is an open source printing system for Linux and other Unix-like operating systems. […]

Read more
Debian 13 — firefox-esr — multiple vulnerabilities (20 CVEs) — patch and remediation guide — diagnosis and fix on Debian 13

Debian 13 — firefox-esr — multiple vulnerabilities (20 CVEs) — patch and remediation guide

🟠 High   ⏱ 15–60 min  Last verified: 28 January 2026 Affected versions: Debian 13 (trixie) 📖 ~4 min read  •  Source: Debian Security Tracker Related CVEs: CVE-2006-2723 CVE-2006-4310 CVE-2006-5462 CVE-2006-5463 CVE-2006-5464 CVE-2006-5633 CVE-2006-5747 CVE-2006-5748  +12 more Upstream summary: Unspecified versions of Mozilla Firefox allow remote attackers to cause a denial of service (crash) via […]

Read more
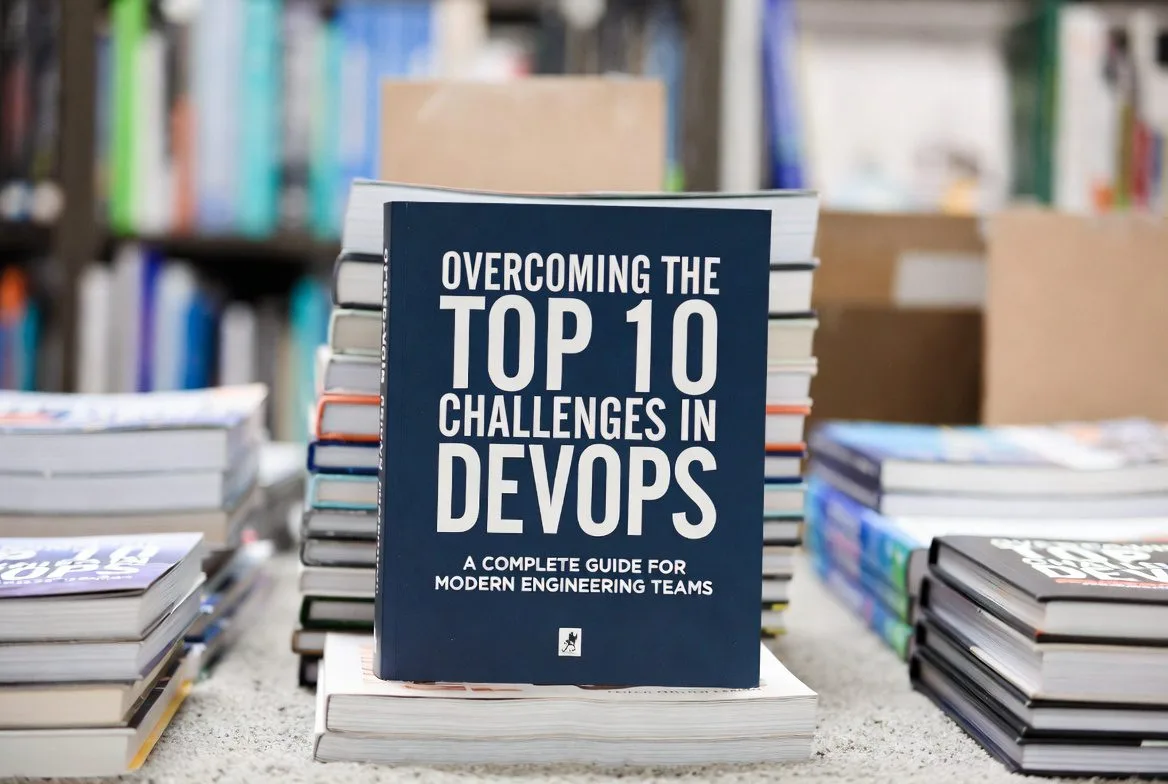
Overcoming the Top 10 Challenges in DevOps: A Complete Guide for Modern Engineering Teams

Overcoming the Top 10 Challenges in DevOps: A Complete Guide for Modern Engineering Teams

Overcoming the Top 10 Challenges in DevOps begins by understanding the foundational philosophy behind this movement. DevOps is not a tool, not a platform and not a single process. DevOps is a way of working that eliminates waste, increases development speed and removes friction between teams that traditionally operated on opposite sides of the delivery pipeline. It blends habits, automation, observability, collaboration and cultural transformation to build, test and ship software faster while making systems more resilient and responsive to change.

Read more
The Best 10 InDesign Plugins, Tools & Add-ons to Try in 2026

The Best 10 InDesign Plugins, Tools & Add-ons to Try in 2026

Adobe InDesign remains the most influential layout and page design platform used by creative agencies, book publishers, marketing departments and production specialists around the world. Its sophisticated typesetting engine, precise layout control and extensive workflow capabilities make it a cornerstone of modern publishing. Yet even with its breadth of built-in features, designers eventually encounter limitations that hinder their ability to automate tasks, streamline production or achieve highly specialized output. This is where InDesign plugins become indispensable.

Read more
FreeBSD 15 — stunnel — multiple vulnerabilities (2 CVEs) — patch and remediation guide — diagnosis and fix on FreeBSD 15

FreeBSD 15 — stunnel — multiple vulnerabilities (2 CVEs) — patch and remediation guide

🟢 Low   ⏱ 5–15 min  Last verified: 27 January 2026 Affected versions: FreeBSD 15 📖 ~4 min read  •  Source: FreeBSD VuXML VuXML topic: stunnel — Remote Code Execution Related CVEs: CVE-2011-2940 CVE-2013-1762 Upstream summary: Michal Trojnara reports: 64-bit versions of stunnel with the following conditions: * NTLM authentication enabled * CONNECT protocol negotiation […]

Read more
NetBSD 10.0 — rustdesk-server — multiple vulnerabilities (3 CVEs) — patch and remediation guide — diagnosis and fix on NetBSD 10.0

NetBSD 10.0 — rustdesk-server — multiple vulnerabilities (3 CVEs) — patch and remediation guide

🟡 Medium   ⏱ 10–30 min  Last verified: 25 May 2026 Affected versions: NetBSD 10.0 📖 ~4 min read  •  Source: pkgsrc audit-packages entry Related CVEs: CVE-2026-30784 CVE-2026-30790 CVE-2026-30796 Upstream summary: pkgsrc audit-packages flagged rustdesk-server-[0-9]* for vulnerability class 'improper-authorization'. Reference: https://nvd.nist.gov/vuln/detail/CVE-2026-30784 Table of contents Symptom & Impact Environment & Reproduction Root Cause Analysis Quick Triage […]

Read more
CHAT